Skip to content

Security implementation

Build protection into the product.

Implement authentication, encrypted connections and data protection around your application. Make security decisions part of how the software works.

Overview

Application security implementation builds protections into the software itself. Our team works on authentication, permissions, transport security, data handling and other controls, with tests for the behaviour those controls are meant to enforce.

What we work on

  • Review sensitive data, user roles and trust boundaries.
  • Implement agreed authentication, TLS and encryption controls.
  • Test access restrictions and document security assumptions.

What you receive

  • Implemented security controls
  • Access control tests
  • Security configuration guidance

What shapes the cost?

Control gaps, application complexity, identity integrations, data handling and verification needs.

What shapes the timeline?

We prioritise the controls by risk and implementation dependencies. Changes to identity or data handling need regression testing across affected user journeys.

What to bring to the first conversation

Application architecture, sensitive data flows, login and permission models, existing findings and deployment constraints.
Selected work

Experience behind the service

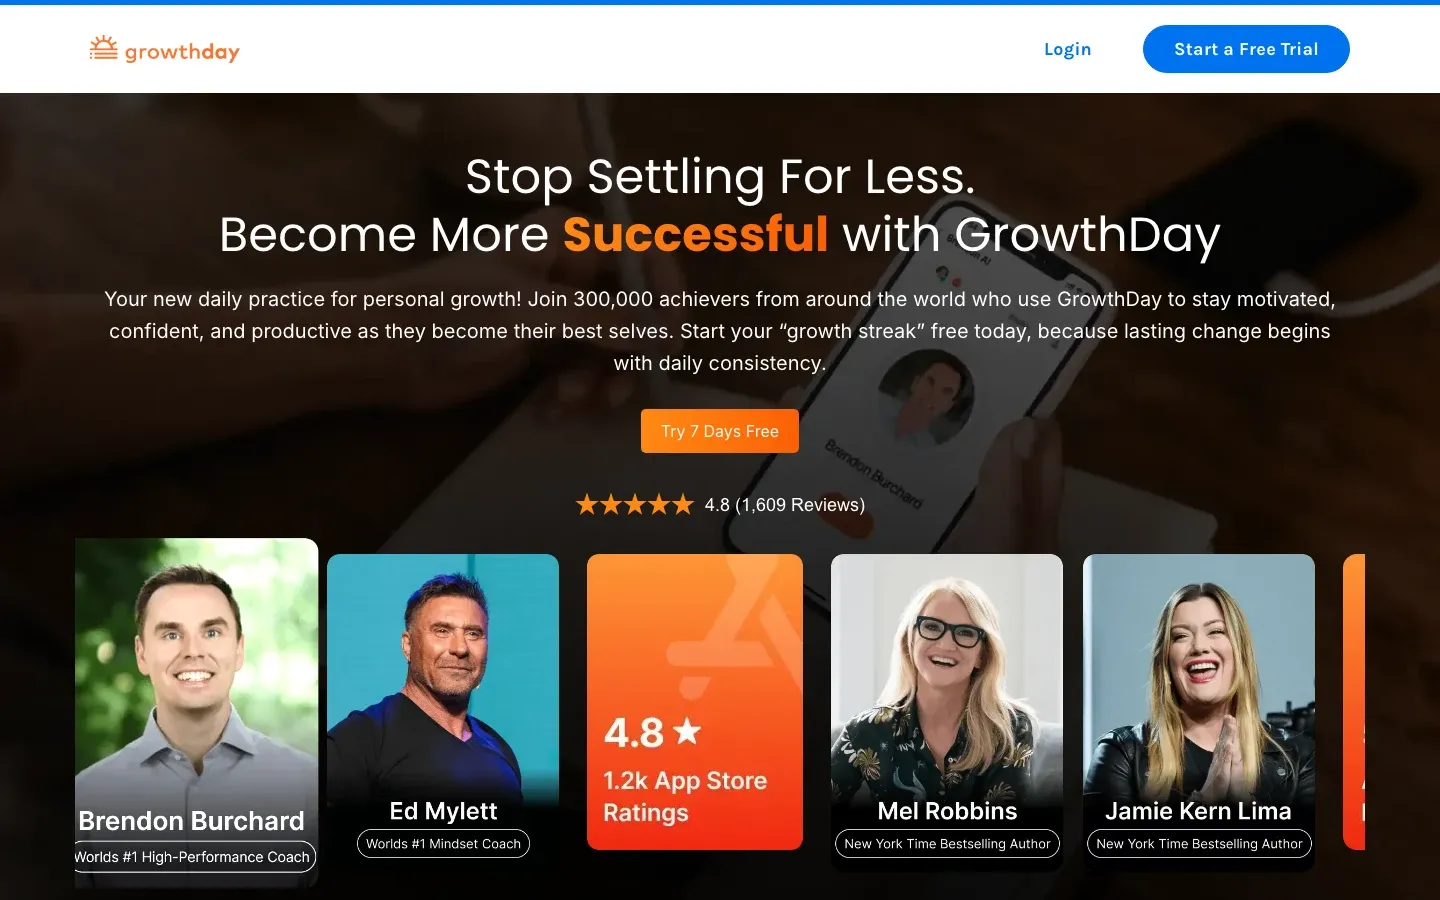
GrowthDay: source portfolio visual
Product engineering

Engineering for a platform that grew to 400K+ users.

Growing a personal development platform meant rebuilding its frontend, improving mobile checkout and giving the enterprise product room to grow.

400K+ Platform users
+9% Checkout conversion improvement

FAQ

Before we get started.

Does this replace a penetration test?

Implementation and independent assessment serve different purposes. A penetration test can be scoped separately to evaluate how the finished controls hold up.

Is HTTPS enough to secure an application?

No. HTTPS protects data in transit, but it does not resolve broken permissions, unsafe input handling or exposed secrets. Our team considers these controls together, based on the application and its threat model.

How do you verify that a security fix works?

Our team tests the intended control and relevant failure cases. For a permission change, that includes requests that should be allowed and denied. Independent penetration testing can provide an additional assessment with its own scope.

Explore services

What's on your mind?

[email protected]